Proxedo API Security

Made in EU API Securityfor webservices that drive EU enterprise

Proxedo API Security combines strict enforcement of cybersecurity policies and ease of use, to address the challenges of securing the ever growing number and complexity of APIs and Webservices.

PAS is a proxy-based API Security Gateway that relies on Deep Packet Inspection of the API payload, enhanced with both negative- and positive security model capabilities to reveal and understand the whole context of payloads.

The Policy-as-Code approach is essential to eliminate attack surfaces beyond common vulnerabilities, and elevate your API security measures to handle Logic-based threats.

The solution supports integration of other security layers such as WAF, Threat Intelligence, SOC, SIEM and DLPS systems and serves as the core of security enforcement in your API ecosystem.
Book a Live Demo

Fields marked with an asterisk are required.

Key Features

  • SOAP & REST API Control

    Full native support for both SOAP & REST APIs

  • Full Payload Check

    Enforce rules on Header & Body contents

  • Encryption

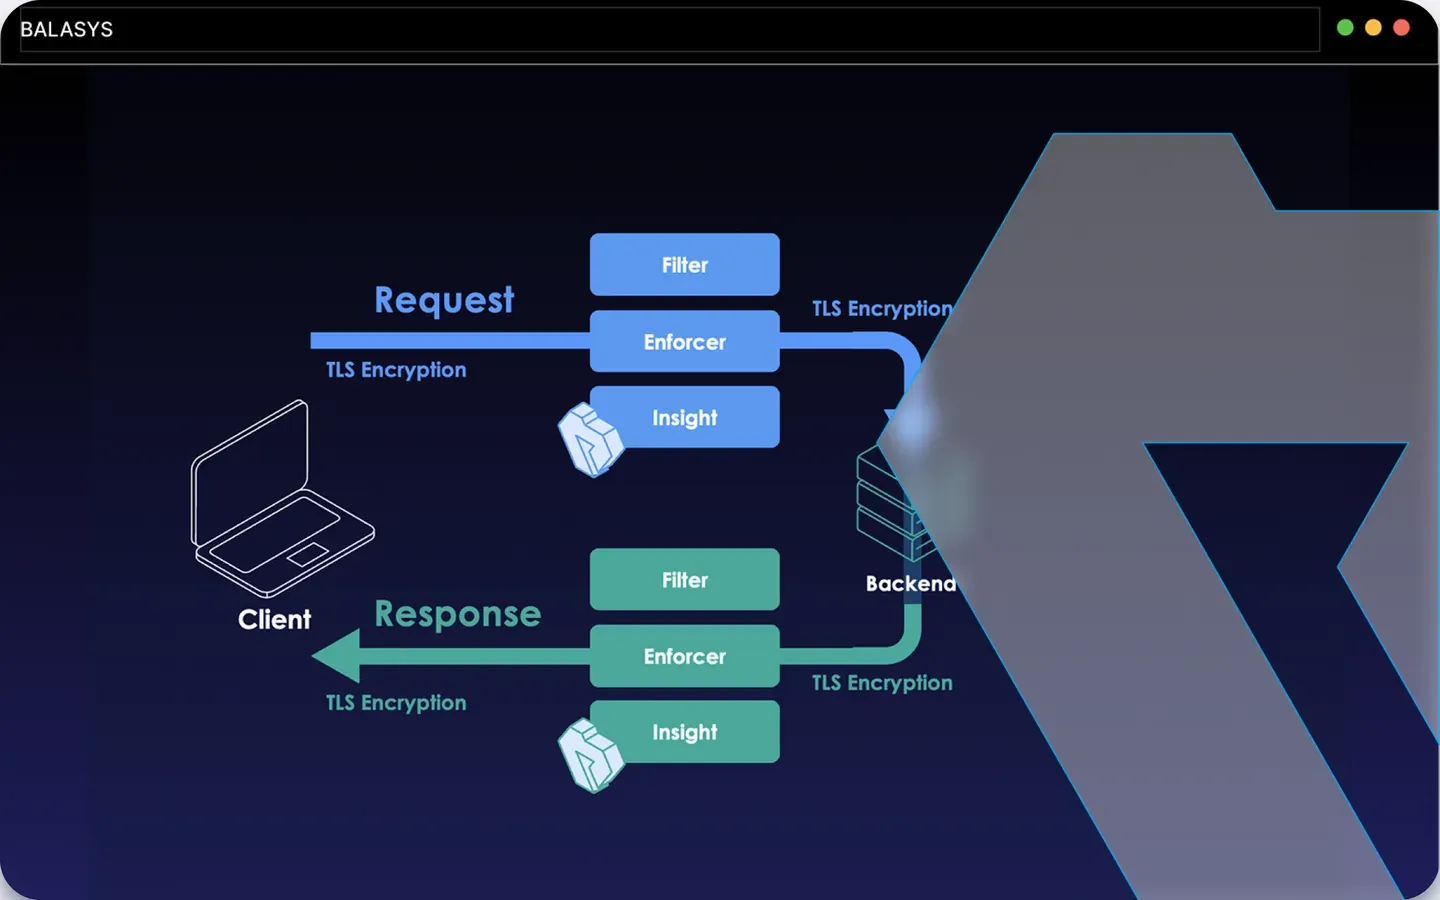
    Enforce TLS Encryption on Client & Backend side

  • Filtering

    Filter Malicious Input & Data Leaks

  • Enterprise-grade Scalability

    Scalable, High-performance, with Central Management

  • Deploy anywhere

    Deploy On-Prem, VM, Cloud or in K8S

A Proxedo API Security flow diagram: client requests and responses passing through Filter, Enforcer and Insight stages with TLS encryption on both sides of the backend
  • Request- and Response

    Create rulesets for both incoming- and outgoing traffic

  • See and Understand

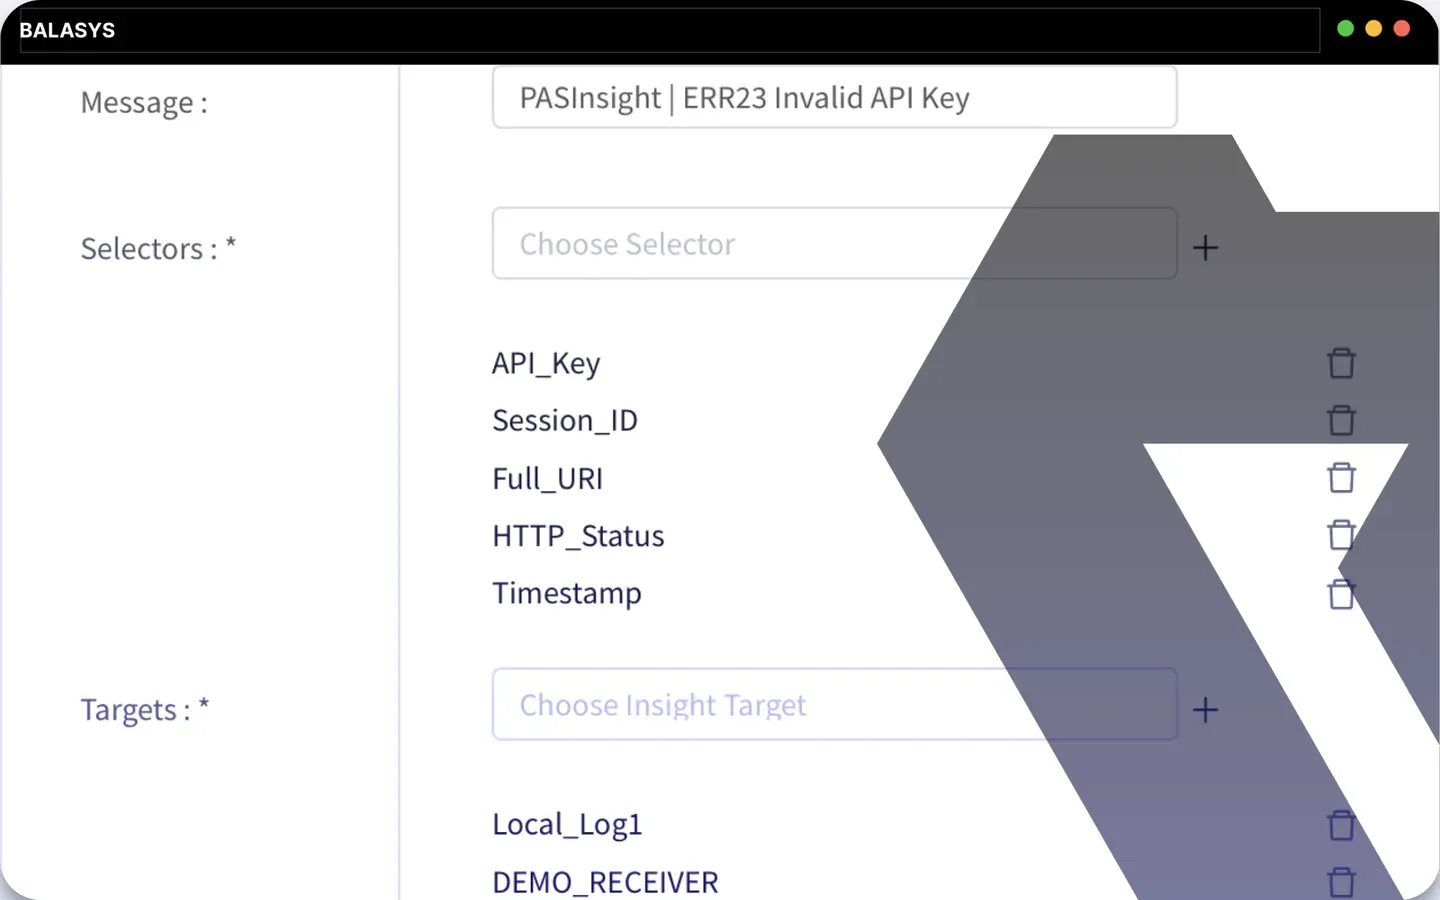
    Log generation based on payload content-aware rules

  • Pre-processing

    Change key labels to match indexes in log targets

  • Forwarding

    Native syslog- and elasticsearch, or local log outputs

  • Secure Transfer

    Encrypt, anonymise and manage log output contents

  • Both Uniform and Unique

    Create & Generate custom log outputs for any use-case

The PAS Insight configuration screen: a log message with its selectors and forwarding targets
  • Schema Validation

    Validate traffic contents against Security Schemas

  • Policy-As-Code

    Enforce Business Logic with fully customisable policies

  • Version-aware rules

    Enforce different rules based on webservice version

  • Perimeter- and Microgateway

    Secure East-to-West and Perimeter traffic

  • Virtual patching on the fly

    Deploy patches, new CVE filters and monitoring rules instantly

  • Publish to the internet with confidence

    Segment internal operations and securely expose services

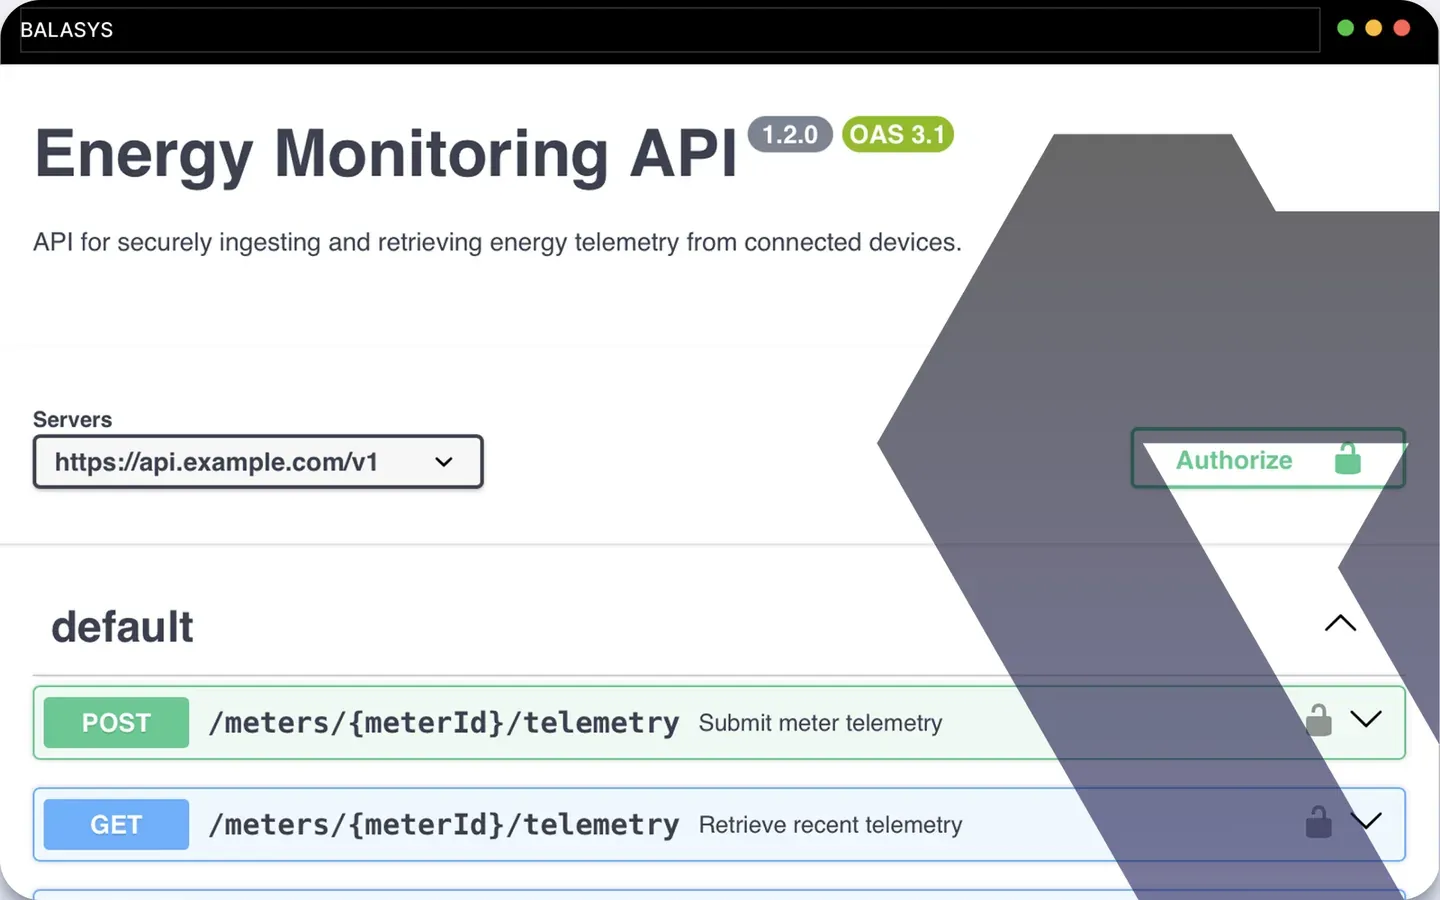
An OpenAPI specification for an Energy Monitoring API, listing its POST and GET telemetry endpoints
  • Backend-Agnostic Gateway

    “Drop-in” deployment into the network, Proxy operation

  • Enhanced Logs

    Gather & Generate logs without added development needs

  • TLS Enforcement

    Enforce Encryption on any Backend without modifying them

  • Logical Segmentation

    Publish services without exposing vulnerable endpoints

  • Performance Rules

    Save performance on the backend by pre-filtering traffic

  • Easy Maintenance

    Save time and resources on maintenance with Schemas

Abstract blueprint artwork captioned “Legacy systems” and “API endpoint”

©2026 Balasys IT Plc.