Syslog-ng & SSB

Enterprise class log managementDiscover syslog-ng and SSB solutions

Whether it’s user activity, performance metrics, Windows events logs, network traffic or any other log data, syslog-ng can collect and centralize log data.

You can remove data silos and gain full-stack visibility of your IT environment. Depending on its configuration, one syslog-ng server can collect more than half a million log message per second from thousands of log sources.

Syslog-ng Store Box™ (SSB) is a high-performance, high-reliability log management appliance.

With SSB, you can search logs, secure sensitive information with granular access policies, generate reports to demonstrate compliance and forward log data to third-party analysis tools.
Book a Live Demo

Fields marked with an asterisk are required.

Key Features

  • Collect & Store

    Full coverage from collection agent to storage

  • Evidence-grade logs

    Secure log pipeline, Tamper-proofing, Trusted Timestamps

  • Mass-storage

    Reduced file-size, massive storage and indexing capabilities

  • Automated rotation rules

    Rotate and Archive logs automatically

  • Enterprise-grade Scalability

    Scalable, High-performance, with Central Management

  • Deploy anywhere

    Deploy On-Prem, VM or in the Cloud

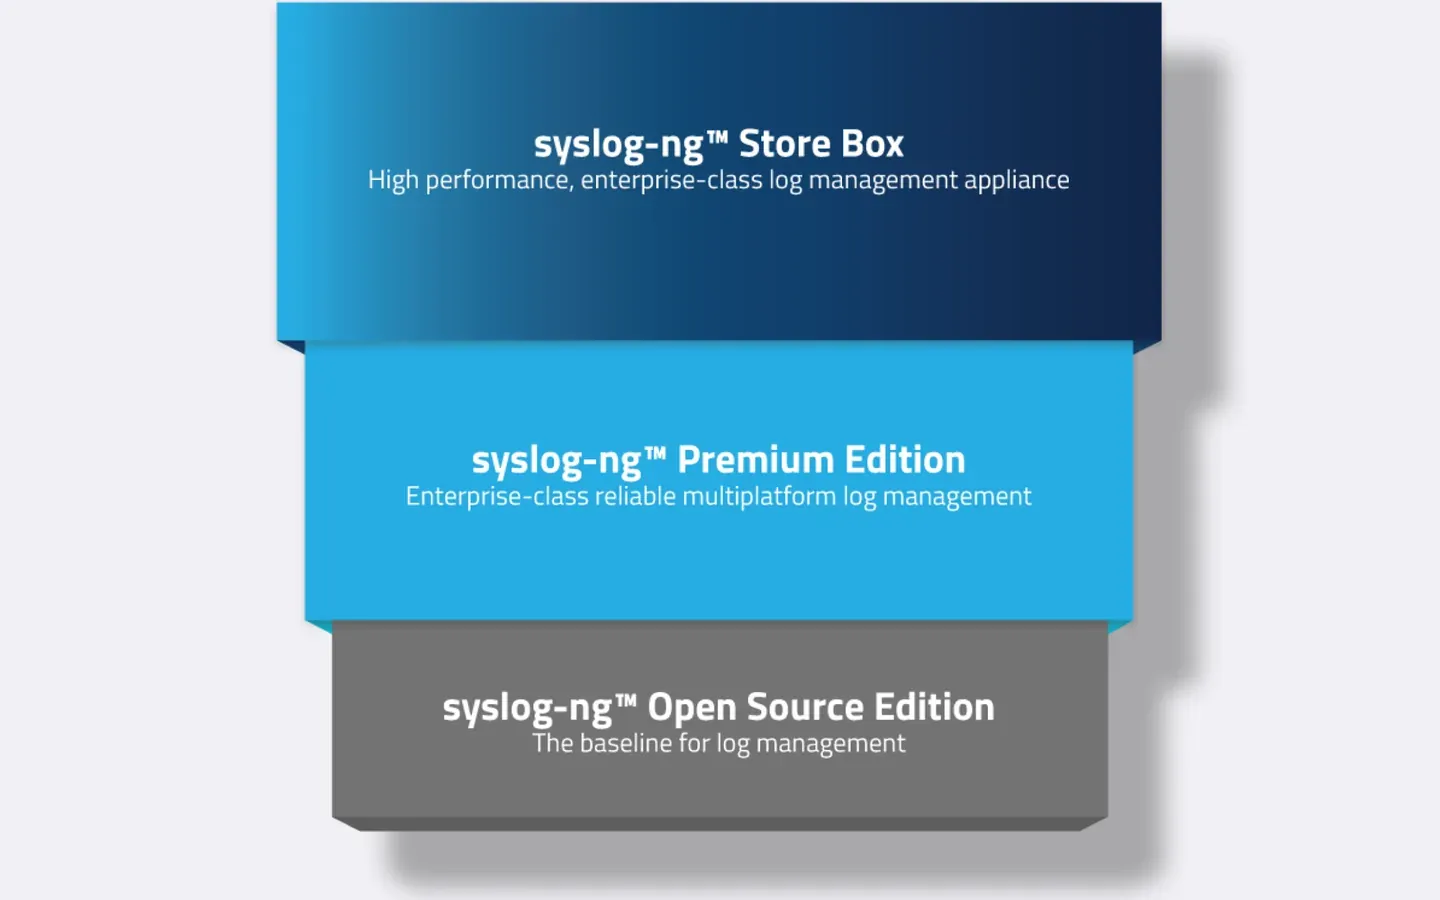
The three syslog-ng editions stacked: Store Box above Premium Edition above Open Source Edition
  • SSB Web GUI

    Intuitive GUI to speed up search with custom views

  • Content-based Alerts

    Get Alerts on important matters, flags and correlations

  • Create Logspaces

    Store logs from multiple sources in dedicated containers

  • Federated Search

    Search information across multiple logspaces

  • Actionable Reports & Alerts

    Start investigations instantly by clicking on alerts

  • Access Control

    Granular Access Management to Logspaces

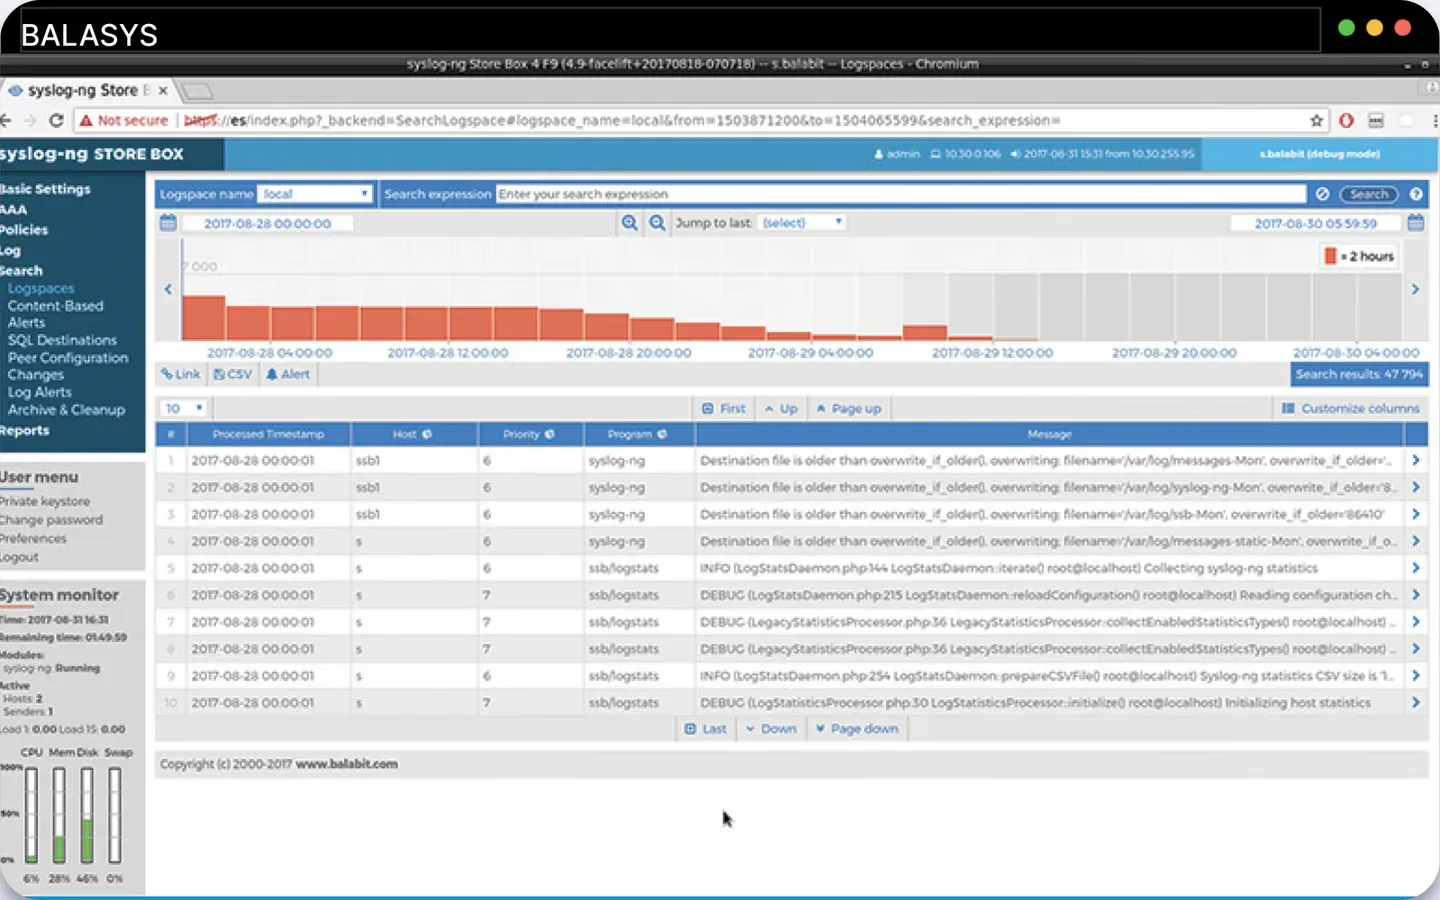
The syslog-ng Store Box web interface: a logspace search with a message-rate histogram over the matching log lines
  • High-Performance

    Index 100 000 Messages or 70Gb raw log data per hour

  • Instant Search

    Index during the ingest process to search immediately

  • 50+ Supported Platforms

    Expand log collection to the whole infrastructure

  • Sort based on Content

    Logspaces automatically store logs based on policies

  • Parse Key-Value and PatternDB Normalize

    Create custom hit rules and normalize logs to fit patterns

  • Message Rate Alerts

    Get notified about quantity be it high- or low

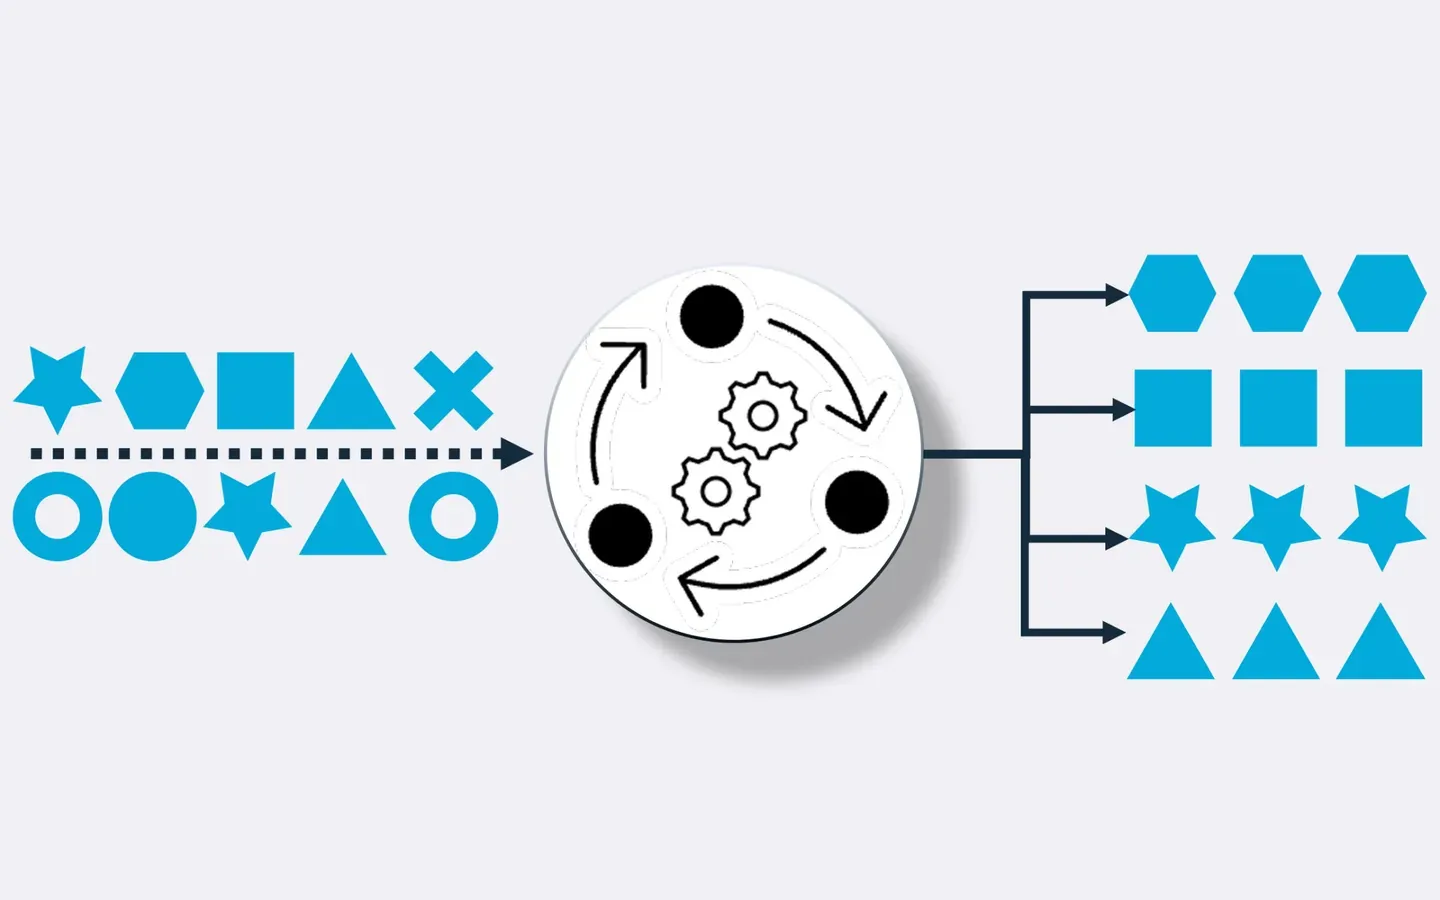
Illustration of mixed log messages entering a processing wheel and leaving it sorted into uniform groups
  • Correlation Rules

    Real-time and content-aware message correlation

  • Automated Log Lifecycle

    Automated log management and forwarding

  • Store & Forward

    Store originals securely, Forward for processing

  • Connect to SOC, SIEM, Big Data and DLPS

    Standard REST API connector for 3rd party log processing

  • PatternDB pre-processing

    Normalize logs for seamless integration with log processing

  • Generate Reports

    Generate Automated Reports for any use-case

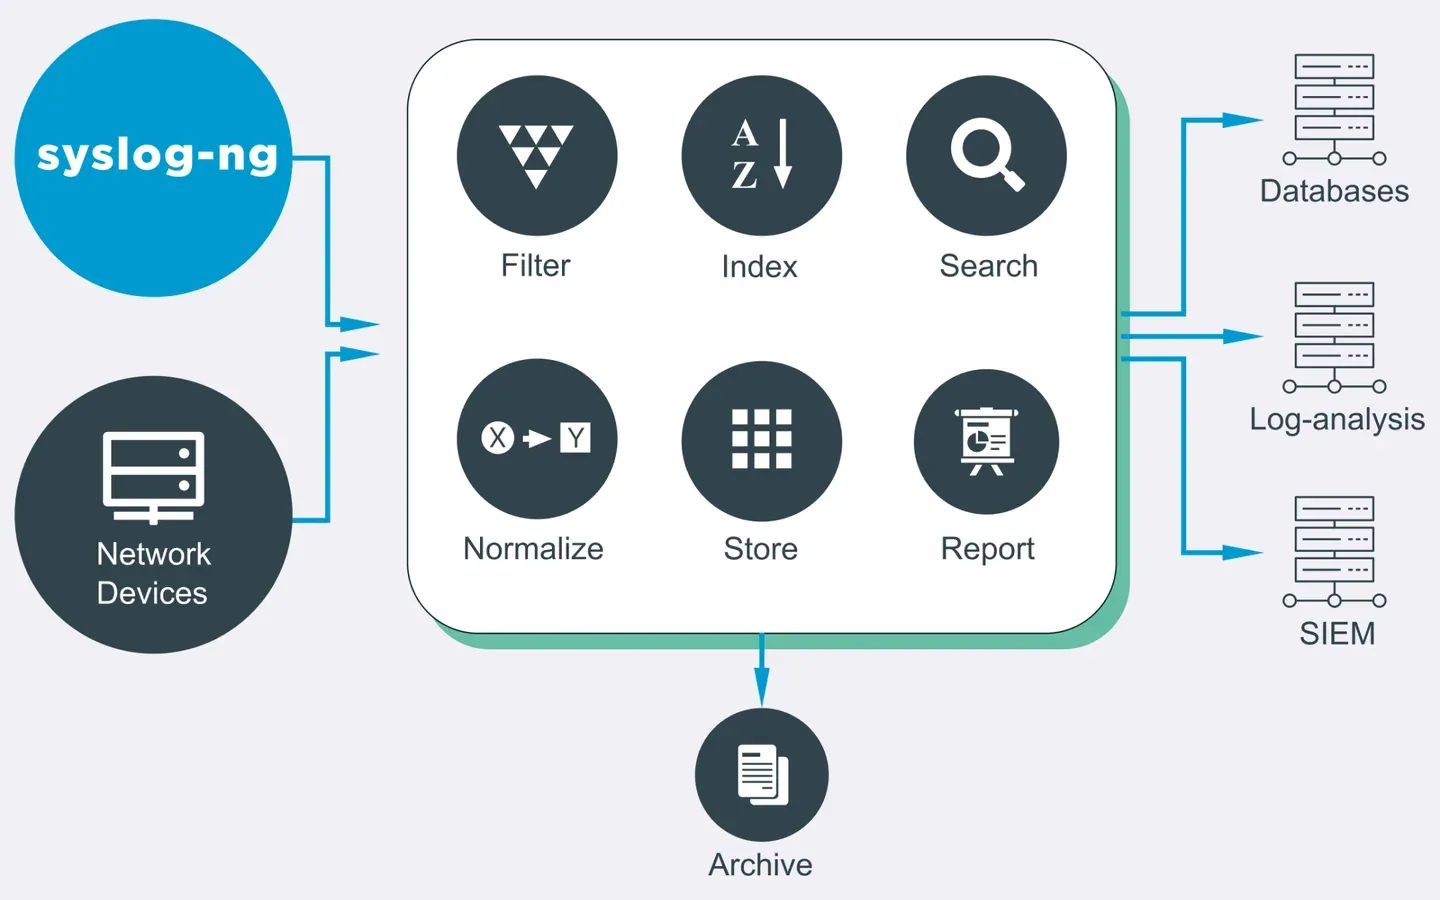
Diagram of syslog-ng filtering, indexing, searching, normalizing, storing and reporting on log data, then feeding databases, log-analysis, SIEM and an archive

©2026 Balasys IT Plc.